Section 40 of IT Act 2000: Generating key pair
Where any Digital Signature Certificate the public key of which corresponds to the private key of that subscriber which is to be listed in the Digital Signature Certificate has been accepted by a subscriber, the subscriber shall generate [that key] pair by applying the security procedure.
Explained:
1. Acceptance of Digital Signature Certificate
The provision applies when a subscriber accepts a Digital Signature Certificate containing a public key corresponding to the subscriber’s private key. The certificate establishes the relationship between the subscriber’s identity and the public key used for verification.
2. Generation of Key Pair
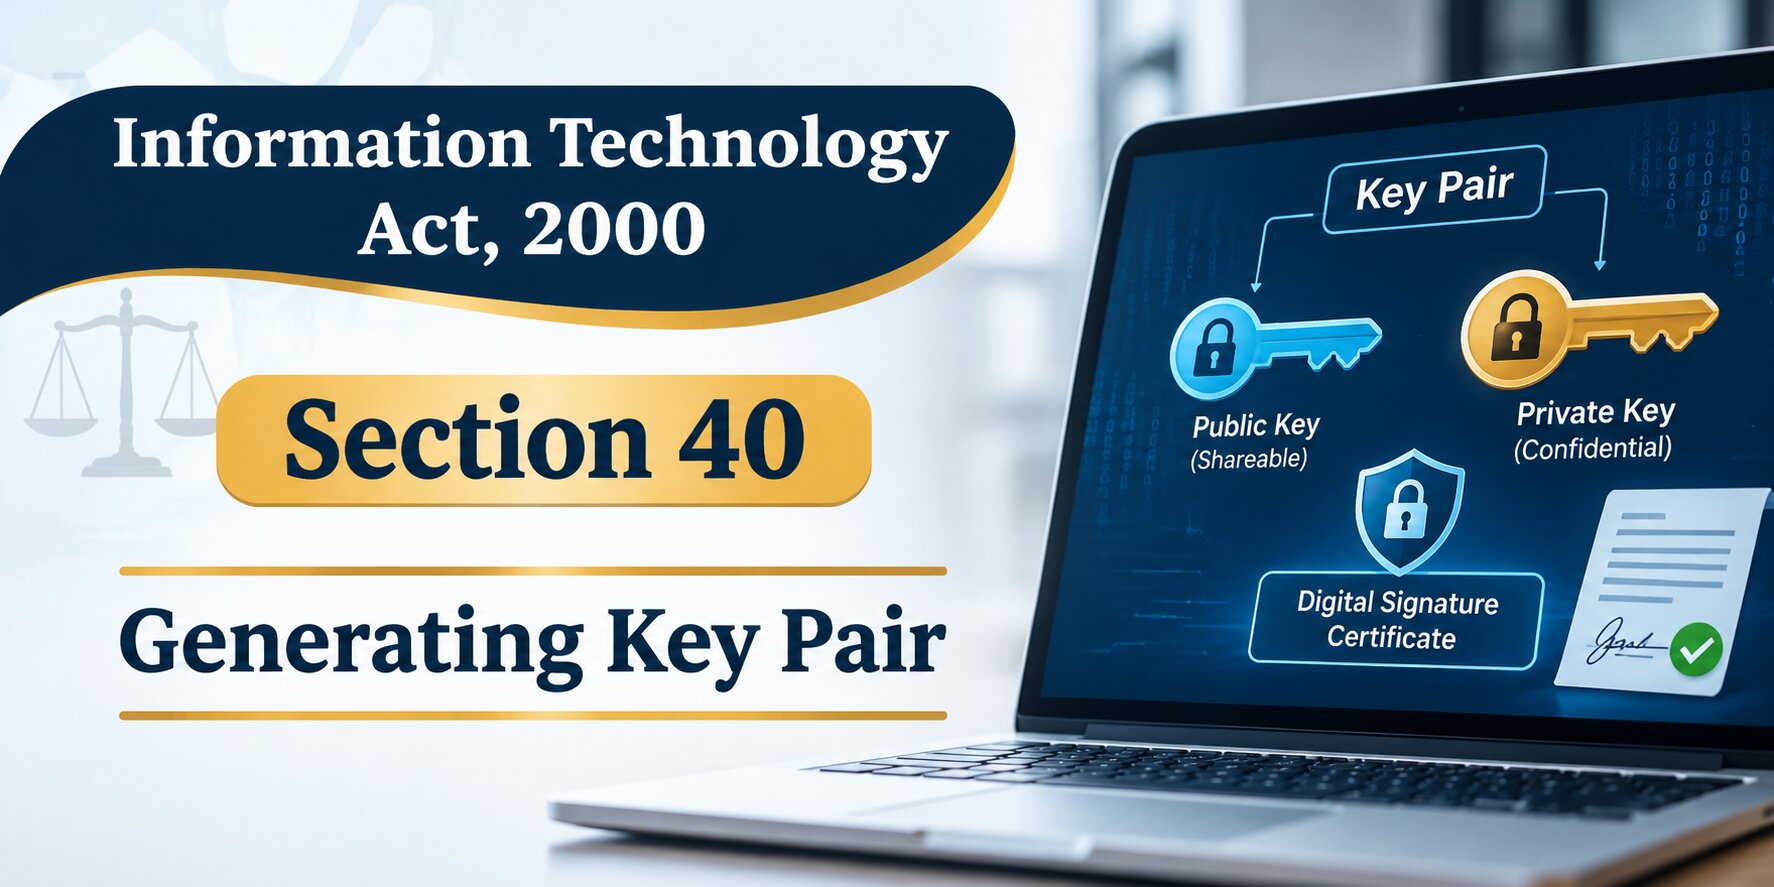
A key pair consists of two cryptographically related keys:
- Public Key: This key can be shared with others and is used to verify a digital signature.
- Private Key: This key remains confidential with the subscriber and is used to create the digital signature.
Both keys work together to establish the authenticity of electronically signed documents.
3. Application of Security Procedure
Section 40 specifically requires the subscriber to generate the key pair by applying the security procedure. This requirement is important because improper generation or handling of cryptographic keys may compromise the reliability of electronic authentication.
The subscriber must take appropriate precautions to protect the private key from unauthorised access, disclosure or misuse.
Importance of Section 40 in Cyber Law
Section 40 strengthens the security framework governing digital signatures in India. It helps establish trust in electronic transactions by ensuring that cryptographic keys are generated through an appropriate security procedure.
The provision is particularly relevant to online banking, electronic tender submissions, government e-filing, corporate transactions and digitally signed agreements. It also complements Sections 35 to 39 of the Information Technology Act, which deal with Digital Signature Certificates and related responsibilities.
Important Judgments
1. Md. Rafat Khan v. Teckinfo Solutions Pvt. Ltd. & Others (Delhi High Court, 2022)
This decision is listed among the judgments associated with Section 40. It may be useful for further research into disputes involving digital authentication and electronic systems. Its specific findings should be checked against the full judgment before relying on it as an interpretation of Section 40.
2. Anvar P.V. v. P.K. Basheer (2014)
The Supreme Court explained the requirements for proving electronic records under the Indian Evidence Act, 1872. Although the case did not directly interpret Section 40, it is relevant to understanding the evidentiary importance of electronic records and their authenticity.
3. Arjun Panditrao Khotkar v. Kailash Kushanrao Gorantyal (2020)
The Supreme Court clarified the requirements for admissibility of electronic evidence under Section 65B of the Indian Evidence Act, 1872. The decision provides useful guidance when digitally generated documents are produced in judicial proceedings.
Conclusion
Section 40 of the Information Technology Act, 2000, establishes an important requirement concerning the generation of cryptographic key pairs by subscribers accepting Digital Signature Certificates. By requiring the application of security procedures, it supports the authenticity and reliability of digital signatures. Understanding this provision is important for businesses, digital certificate subscribers, legal professionals and students studying Indian cyber law.
Leave a Reply