Section 27 of IT Act 2000:
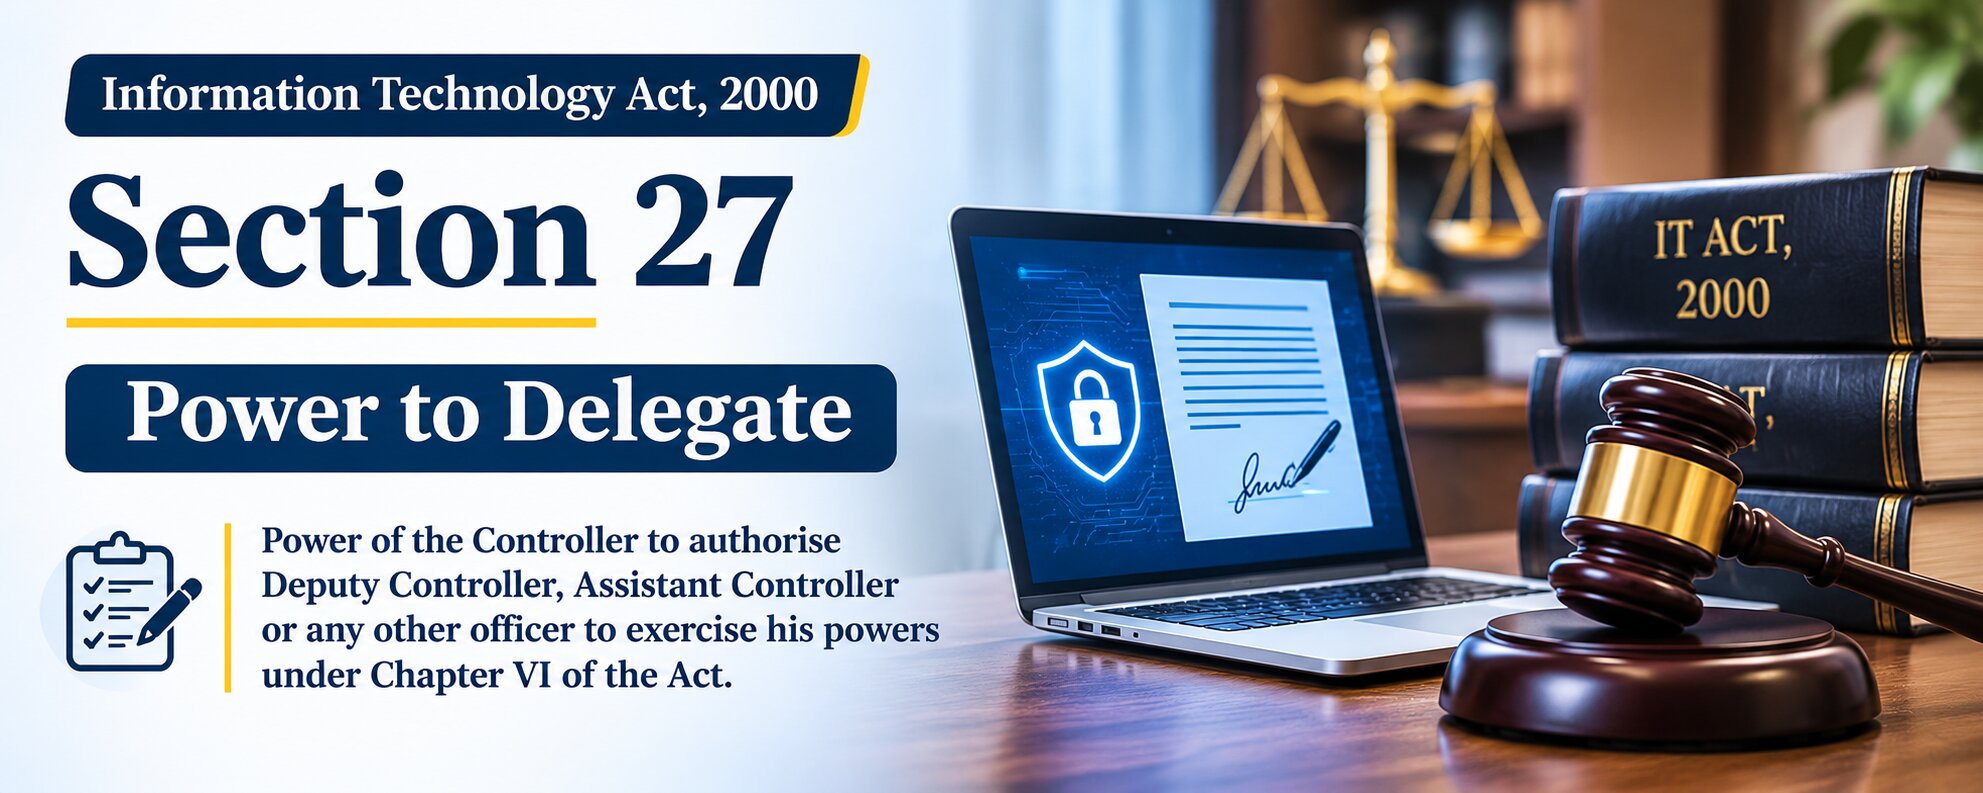
The Controller may, in writing, authorise the Deputy Controller, Assistant Controller or any officer to exercise any of the powers of the Controller under this Chapter.
Explained:
1. Power of the Controller
The Controller of Certifying Authorities is responsible for performing regulatory functions under the Information Technology Act, 2000. These functions relate to the regulation and supervision of Certifying Authorities.
Section 27 enables the Controller to distribute certain responsibilities among authorised officers instead of personally performing every administrative function.
2. Written authorisation is mandatory
The expression “in writing” is particularly important. Delegation under this section must be supported by written authorisation. An officer cannot simply assume the Controller’s powers without proper authority.
Written authorisation helps establish the scope of delegated responsibility and provides accountability in the exercise of statutory powers.
3. Officers eligible for delegation
Section 27 identifies three categories of persons who may receive delegated powers:
- Deputy Controller: May exercise powers formally delegated by the Controller.
- Assistant Controller: May perform authorised regulatory and administrative functions.
- Any officer: Another officer may also receive delegated powers through written authorisation.
4. Delegation is limited to Chapter VI
The words “under this Chapter” restrict the scope of delegation. The provision does not authorise officers to exercise every power available to the Controller under the entire Information Technology Act.
The delegated authority must remain within the powers conferred by Chapter VI and the terms of the written authorisation.
Importance of Section 27 in Cyber Law
Section 27 helps maintain administrative efficiency in regulating Certifying Authorities. Its practical importance includes:
- Administrative efficiency: Enables the Controller to distribute regulatory responsibilities among authorised officers.
- Effective supervision: Helps ensure that regulatory functions under Chapter VI can be performed efficiently.
- Accountability: Written authorisation establishes the legal authority of officers exercising delegated powers.
- Continuity of administration: Prevents regulatory work from depending entirely on the personal availability of the Controller.
Important Judicial Decisions
There is no well-established reported Supreme Court judgment directly interpreting Section 27 of the Information Technology Act. However, the following decisions explain important principles of statutory delegation.
1. Sahni Silk Mills (P) Ltd. v. Employees’ State Insurance Corporation (1994)
The Supreme Court examined whether an authority that had received delegated powers could further delegate those powers to another officer.
Relevance: The Court explained that sub-delegation is generally not permitted unless expressly authorised by the statute or necessarily implied. This principle is relevant when interpreting the limits of written delegation under Section 27.
2. Harishankar Bagla v. State of Madhya Pradesh (1954)
The Supreme Court considered the validity of delegated legislative powers under the Essential Supplies (Temporary Powers) Act, 1946.
Relevance: The judgment explains that delegation may be legally permissible when the parent legislation establishes the framework and identifies the authorities empowered to exercise delegated functions.
These decisions provide useful guidance for understanding the legal limits of delegation under statutory provisions. Indian Kanoon+1
Conclusion
Section 27 of the Information Technology Act, 2000, provides the Controller of Certifying Authorities with the statutory power to delegate functions to a Deputy Controller, Assistant Controller or another officer through written authorisation.
Although the provision contains only one paragraph, it plays an important role in the administration of electronic authentication and the regulation of Certifying Authorities in India. Its central requirement is that delegated powers must be exercised by officers who have received proper written authority and only within the scope permitted by Chapter VI.
Leave a Reply